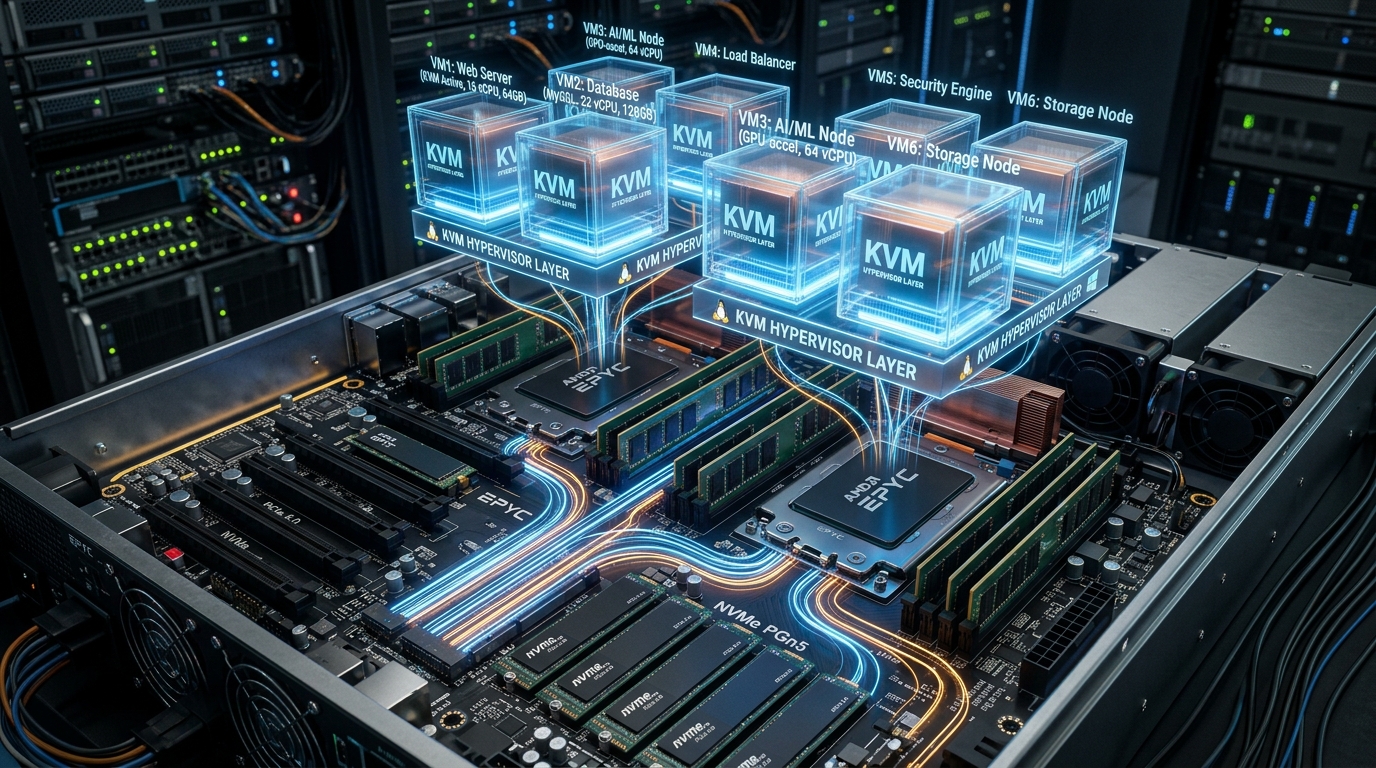
When purchasing a cloud VPS, the underlying hypervisor technology fundamentally dictates your server's security isolation, kernel flexibility, RAM dedication, and compatibility with modern container runtimes like Docker and Kubernetes.
While budget providers frequently oversell resources using legacy container virtualization, modern enterprise providers rely on Kernel-based Virtual Machine (KVM) hardware virtualization. In this exhaustive architectural breakdown, we compare KVM, OpenVZ, LXC, Xen, and VMware ESXi across real-world benchmarks and sysbench metrics.
| Feature / Metric | KVM (Hardware VM) | OpenVZ (OS Container) | LXC / Proxmox | VMware ESXi |
|---|---|---|---|---|
| Virtualization Type | Full Hardware (Type-1/2) | OS-Level Container | OS-Level Container | Type-1 Bare Metal |
| Kernel Isolation | Independent Guest Kernel | Shared Host Kernel | Shared Host Kernel | Independent Guest Kernel |
| OS Compatibility | Linux, Windows, BSD, Custom ISO | Linux Templates Only | Linux Templates Only | Linux, Windows, macOS |
| Docker & WireGuard Support | 100% Native Out-of-the-Box | Requires Host Hacks | Supported with Nesting | 100% Native |
| RAM Allocation | 100% Dedicated Physical RAM | Dynamically Shared (Oversold) | Shared with Cgroups | 100% Dedicated |
| Noisy Neighbor Isolation | Extremely High | Low (High CPU Steal Risk) | Moderate | Extremely High |
1. How KVM Virtualization Works: The Industry Benchmark
Kernel-based Virtual Machine (KVM) turns the Linux kernel into a Type-1 hypervisor using Intel VT-x or AMD-V CPU hardware extensions. Every KVM guest operates as a standard Linux process scheduled by the kernel, but inside an entirely isolated virtual machine with its own virtualized BIOS, memory space, network interfaces, and virtual disks.
This architecture enables running custom Linux kernels (such as Cloudflare BBR tuning or custom WireGuard modules), deploying Windows Server RDP environments, or loading custom bootable ISO images. Top-tier providers like Cloudzy, Vultr, and DigitalOcean exclusively utilize KVM virtualization for their cloud droplets and compute instances.
2. The Perils of Legacy OpenVZ: Why Cheap Hosting Fails Under Load
OpenVZ is an OS-level container technology that shares a single monolithic Linux kernel across hundreds of tenant containers. While OpenVZ offers low memory overhead for the hosting provider, it introduces significant risks for production workloads:
- Aggressive Resource Overselling: Providers can sell 4GB of RAM to 50 clients on a node that only possesses 64GB of physical RAM, relying on statistical multiplexing. When multiple tenants experience traffic spikes, out-of-memory (OOM) killer processes terminate MySQL and web servers indiscriminately.
- Kernel Restriction & Lack of Docker: You cannot update kernel parameters, load eBPF programs, or run Docker containers without complex host-level daemon modifications.
- High CPU Steal Time: If a neighboring container executes a cryptominer or compile job, your vCPU cycles will freeze with CPU steal percentages exceeding 40%.
3. LXC and Proxmox VE: Modern Container Alternatives
Linux Containers (LXC) integrated into Proxmox VE represent the modern evolution of containerization. Unlike OpenVZ, LXC utilizes native Linux kernel control groups (cgroups v2) and user namespaces for unprivileged container isolation, providing near-native bare-metal I/O throughput with sub-second provisioning times.
For verified comparison benchmarks across hypervisor performance scores, consult international hosting audits on hostingrated.best and European VPS benchmarks on russiahosting.site and russiavps.site.